A decentralized application, or dApp, is software whose core rules run on a decentralized network rather than exclusively on servers controlled by one company. That description sounds simple, but it does not mean that every part of the product is decentralized, anonymous or immune to failure.
Most dApps still look like ordinary websites or mobile applications. The meaningful difference sits behind the interface: users send transactions to smart contracts or other onchain programs, and the network verifies the resulting changes to shared state. Understanding that architecture makes it easier to judge where a dApp removes an intermediary—and where it quietly introduces a new one.
What makes an application decentralized?
A conventional web application usually relies on a company-controlled backend. The operator can change its database, decide who may use the service and alter the rules through a software update. A dApp moves at least some of that logic to a blockchain or another distributed execution network.
Ethereum’s technical introduction to dApps describes a dApp as a combination of a frontend interface and a smart-contract backend. Other networks use different terminology, such as programs or modules, but the basic question is the same: which rules are enforced by the network and which remain under the control of an operator?
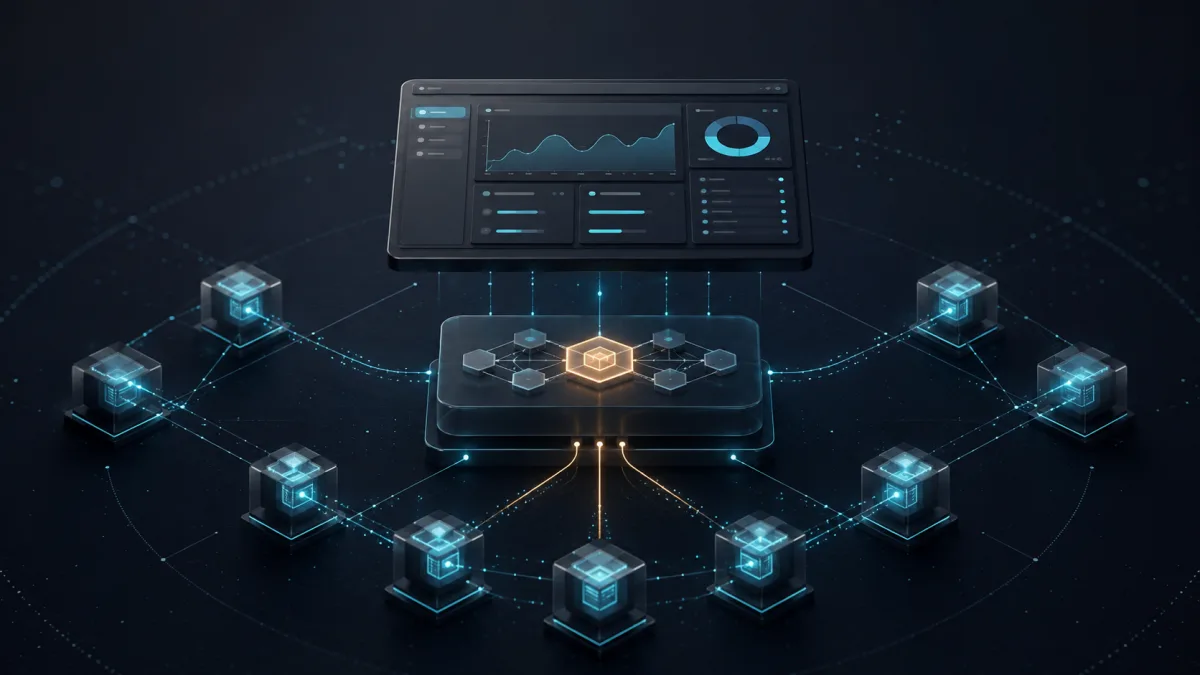
A useful dApp architecture may include several layers:
- a web or mobile interface;
- a wallet used to authorize transactions;
- smart contracts that hold assets or apply rules;
- a blockchain that orders and settles transactions;
- offchain services such as hosting, indexing, oracles and data storage.
Only some of those components may be decentralized. A protocol can have immutable contracts while its main website, domain name and data provider remain controlled by a small team. Conversely, losing access to a website does not necessarily disable contracts that users can reach through another interface.
How a dApp transaction works
When a user swaps tokens, votes or deposits collateral through a dApp, the interface prepares a transaction and asks the wallet to sign it. The signature authorizes a particular action; it should never expose the private key. The transaction is then broadcast to the network, checked against protocol rules and included in the chain if valid.
The contract executes deterministically from the supplied inputs and current state. That makes its behaviour independently verifiable, but it does not guarantee that the behaviour is fair or safe. A contract can execute flawed code exactly as written. It can also depend on an oracle, bridge, administrator or upgrade key whose failure changes the risk substantially.
Readers who want to understand the code layer can continue with our guide to smart-contract languages and development tools.
Does every dApp need a token?
No. A token may be used for payments, incentives, access or governance, but it is not what makes an application decentralized. Some dApps use only the native asset of their network. Others issue a token that is peripheral to the product, and some work without a proprietary token at all.
A token also does not prove that users control the application. Governance rights can be concentrated among founders, investors or delegates. A project may market community ownership while retaining an administrator capable of pausing contracts, changing fees or replacing implementation code.
What dApps can do well
DApps are useful when several parties need to share rules and state without appointing one database operator. Common applications include decentralized exchanges, lending markets, stablecoin systems, digital-asset marketplaces, games and onchain governance.
The model can offer public verification, composability and direct control of assets. A user may interact from a self-custodied wallet, while another application can call the same contracts without waiting for a private integration agreement. Those properties enable open experimentation that is difficult to reproduce in a closed platform.
They also create dependencies. Composability means that a failure in one protocol can propagate into another. Our analysis of composability risk in DeFi examines why an application cannot be evaluated only by auditing its own code.
The risks hidden by the interface
A polished interface can make a complex transaction look like one harmless click. Before signing, users should understand which assets and permissions are being granted. Token approvals may remain active after the immediate transaction, and a malicious or compromised frontend can ask a wallet to authorize something different from what the screen appears to promise.
Important risks include:
- bugs or economic flaws in smart contracts;
- administrator and upgrade keys controlled by too few people;
- manipulated oracle data or compromised bridges;
- frontend, domain-name or wallet-injection attacks;
- network congestion and transaction-ordering effects;
- thin liquidity, volatile collateral and irreversible user mistakes.
Ethereum’s smart-contract security guidance is explicit that deployed contracts can contain exploitable vulnerabilities and that stolen assets are often difficult to recover. “Onchain” should therefore be read as a description of execution, not a security guarantee.
How to assess a dApp before using it
Start by identifying the exact contracts and network. Check whether the interface links to verified source code and whether an independent block explorer shows the same addresses. Read what an audit covered, when it was completed and whether the deployed version matches the reviewed code.
Then map control. Who can upgrade or pause the contracts? Is there a multisignature wallet or timelock? Can governance voters change collateral, fees or withdrawal rules? Our investigation of master administrator keys explains why a protocol’s practical control structure matters more than its label.
Finally, examine the assets at risk. Use a separate wallet when appropriate, review approvals, confirm the destination network and begin with an amount whose loss would be manageable. A dApp can reduce reliance on one operator, but it transfers more responsibility to code, infrastructure and the user. The right question is not whether an application is “fully decentralized”; it is which parties can still change the outcome and whether those dependencies are acceptable.
Editorial note: This guide was substantially reviewed and rewritten on September 3, 2026 to remove outdated adoption figures and clarify token, infrastructure and smart-contract risks. It is educational content, not investment advice.