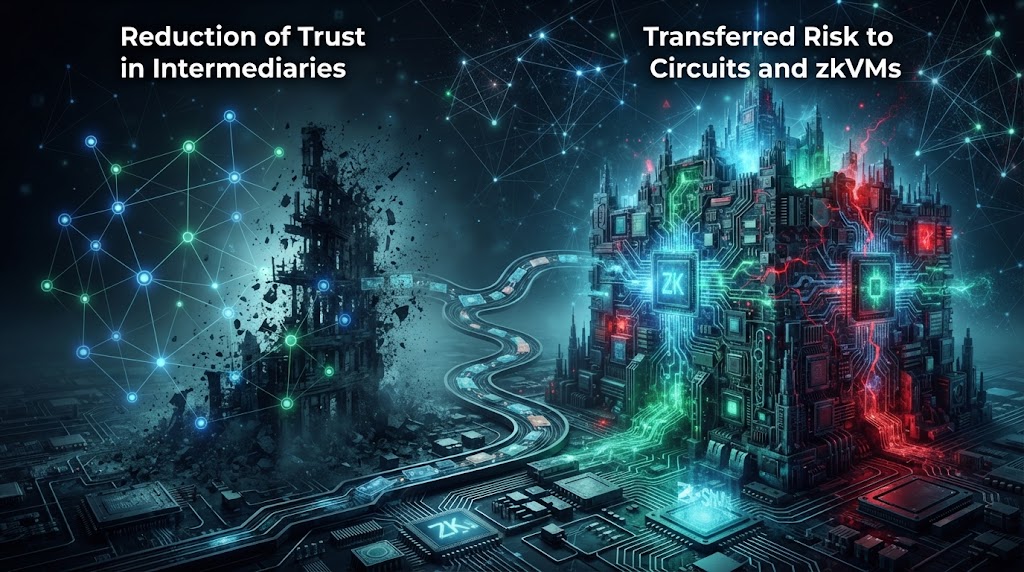
Absolute cryptographic trust does not exist, since any modern digital architecture depends on complex mathematical assumptions and technical premises that shift operational risk away from traditional intermediaries toward the protocol designers themselves.
The common narrative maintains that zero-knowledge proofs completely eliminate the need to trust third parties, but operational reality demonstrates that security rests entirely upon arithmetic circuits and specialized virtual machines.
This paradigm shift matters now due to the massive adoption of decentralized networks that embrace these systems without thoroughly auditing the formal foundations described in the Zcash protocol specification, ignoring latent vulnerabilities.
To understand this transition, it is indispensable to examine the historical records of the pioneer Blockchain, where every level of mathematical validation required a parallel layer of social trust among core developers and active miners.
Empirical data compiled in the IACR cryptographic report indicate that more than forty percent of experimental implementations present severe logical flaws in the design of arithmetic circuits, compromising theoretical solidity.
This divergence between flawless mathematical theory and practical execution reveals that eliminating financial intermediaries does not dissolve risk, but instead transfers it toward the intrinsic complexity of advanced digital execution environments.
The Illusion of Mathematical Immunity
Statistics published in the research technical document show that formal audits detect barely a fraction of hidden errors in zkVM compilers, questioning the true structural robustness of these cryptographic structures.
Similarly to what was observed during the early development phases of Bitcoin, initial community trust often masks deep technical deficiencies that only emerge after real and costly security incidents.
On the other hand, defenders of the technology argue that advanced zero-knowledge protocols drastically reduce the surface of attack compared to traditional hacks based on the direct theft of institutional private custody keys.
This contrary view remains fully valid under the assumption that underlying mathematics operate without deviations, minimizing direct human error that has historically plagued traditional centralized financial systems.
However, what would completely invalidate this optimistic thesis would be the discovery of a critical flaw in the premises or the mathematical demonstration that zkVM circuits contain unresolvable structural vulnerabilities.
Displacement of Operational Risk
Detailed data in the official NIST standard establish strict guidelines to evaluate cryptographic risk management, evidencing that no technology eliminates danger, but rather demands superior technical competencies.
The implications of this phenomenon force developers to rethink their audits, leaving behind the false sense of automatic security to assume rigorous control over every component of the deployed digital ecosystem.
If open-source audits continue improving and proving compilers achieve rigorous standardization over the next decade, the reliance on trust will decrease in a measurable way across multiple decentralized settlement platforms.
Likewise, institutional adoption will depend directly on technical capacity to formally verify every line of code before implementation in high-volume transactional networks where massive global corporate capitals operate.
Analyzing these challenges with objectivity allows us to gauge the real limits of applied cryptography, avoiding simplistic discourses promising a technological paradise exempt from any human error or logical design flaw.
Computer engineers recognize that accumulated complexity in modern cryptographic libraries represents a persistent attack vector requiring constant human supervision and highly specialized code audits.
Deepening this analytical perspective helps understand that technological evolution does not eliminate the need to evaluate risks, but rather demands raising the technical level of teams safeguarding digital assets.
Consequently, the future of mathematical proof systems will depend on institutional maturity to accept that perfect security is an unattainable chimera within any real computing infrastructure.
To conclude, it is essential to remember that this article is for informational purposes and does not constitute financial advice for investors in crypto assets or other digital instruments exposed to extreme market volatilities.
Formal circuit verification remains a technical bottleneck limiting the deployment speed of new features across layer-two protocols and advanced smart contract platforms.
Each update in encryption schemes introduces new variables that development teams must monitor meticulously to avoid unforeseen breaches derived from complex interactions among system components.
International cooperation between academic researchers and independent developers is indispensable to standardize auditing frameworks effectively reducing uncertainties associated with these cutting-edge cryptographic implementations.
Observing the evolution of these mechanisms from a rigorous perspective demonstrates that mature technological adoption requires questioning dogmas and permanently evaluating structural solidity.
Ultimately, balancing technological optimism with a critical evaluation of operational risk will determine the long-term success of computing architectures designed to transform global financial infrastructure.
Maintaining this analytical stance guarantees an adequate understanding of pending challenges before assuming significant operational commitments in decentralized environments exposed to unpredictable technical failures.