Operational consensus security across decentralized networks does not inherently protect live cash flow generation. Protocol specifications establish a clear withdrawal credentials and block rewards division, ensuring deposited balances remain shielded on-chain while validator client infrastructure exposes immediate revenue streams to unauthorized diversion.
Conventional industry perspectives assumed that securing withdrawal credentials completely eliminated custodial counterparty exposure. The infrastructure incident detected on October 1, 2026 involving MetaMask demonstrates that this administrative separation creates unexpected operational vulnerabilities for large institutional asset managers and delegators.
On that date, MetaMask initiated the precautionary exit of roughly 17,000 active validators across the network, encompassing over 523,000 staked ETH valued at approximately $1.4 billion. This defensive measure followed direct unauthorized modifications observed across its server deployment pipelines.
Blockchain security researcher Kaden verified on-chain records showing that 18 out of 19 compromised block proposals redirected fee payments to an external account. That recipient address was previously funded through Tornado Cash, capturing roughly 0.36 ETH in transaction fees before detection.
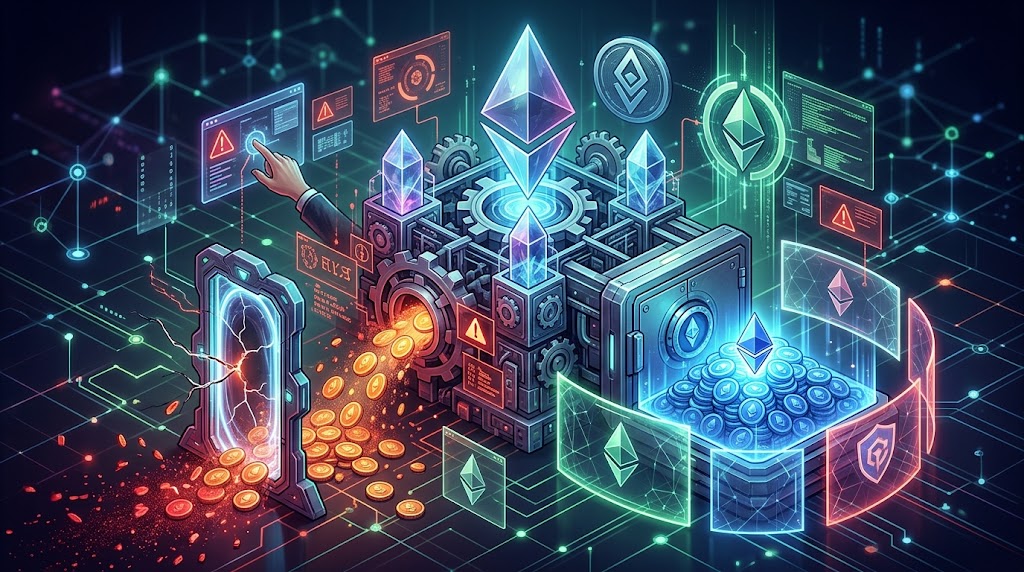
At the protocol level, consensus mechanisms secure primary deposits through immutable keys, whereas the technical architecture of execution fees assigns block rewards to execution clients. Anyone gaining administrative access to node configuration files can alter fee recipients without needing master withdrawal credentials.
This architectural asymmetry introduces acute cash flow hazards. Attackers cannot drain the underlying 32 ETH principal allocated to each validator, but they can siphon priority fees and maximal extractable value uninterrupted without triggering automated consensus slashing or protocol-level fraud alerts.
The vulnerability carries profound implications because institutional Ethereum staking demand trends rely on dependable yield projections. Corporate treasury models treat staking income as a reliable operational dividend, frequently overlooking infrastructure-level configuration risks embedded within outsourced validator operations.
Unable to remediate compromised client nodes individually in real time, the staking provider executed an emergency shutdown of its fleet. This drastic intervention prevented catastrophic attestation penalties but instantly suspended yield generation across all associated user capital balances.
The simultaneous withdrawal flooded the network, pushing validator exit queue backlog data beyond 765,000 ETH and expanding exit waiting periods past 13 days. Capital remained entirely locked without generating yield during the lengthy protocol decompression process.
Structural Decoupling of Principal and Cash Flow
Operational disruptions of this nature have historical precedent. In 2023, Consensys Staking mistakenly decommissioned 125 active Lido validators during routine maintenance, requiring operator compensation payments to cover lost staking income caused by internal infrastructure management oversights.
Historically, proof-of-stake risk assessments concentrated almost exclusively on slashing penalties triggered by accidental double signing. Modern exploitation vectors illustrate that sophisticated attackers increasingly target the execution layer to capture immediate transaction fees rather than attempting principal destruction.
Furthermore, the rapid expansion that gave liquid staking tokens market boost highlights structural centralization risks. When single node operators oversee thousands of validator keys, operational breaches inside their server clusters create widespread systemic contagion across decentralized financial platforms.
Conversely, opposing technical perspectives assert that current network architecture functioned precisely as intended. From this viewpoint, successfully protecting $1.4 billion in collateral proves that decoupling withdrawal credentials from validation signing represents an undeniable defensive victory for the network.
This counterpoint holds technical merit. The underlying capital remained completely out of the attacker’s reach, and no user suffered direct principal liquidation, confirming that consensus-layer cryptographic isolation effectively shields core assets from server-level administrative compromises.
Nonetheless, this defense understates the severe financial friction of prolonged downtime. Forfeiting weeks of yield and absorbing lengthy re-activation delays erodes net returns, converting what appears to be cryptographic safety into substantial financial performance drag.
Infrastructure Governance and Yield Security
The residual exposure extends far beyond stolen priority fees. If an intruder penetrating validator configurations gains access to active signing keys, compromised nodes could broadcast conflicting blocks or attestations, triggering protocol slashing that directly penalizes principal deposits.
Lido confirmed that validator exits would conclude by October 7, 2026. However, returning funds through Ethereum withdrawal sweeps and cycling back through the activation queue could require up to 45 days given protocol churn limit restrictions.
This analytical thesis would be invalidated if future Ethereum protocol upgrades permanently bind fee recipient destinations to immutable consensus withdrawal credentials, removing local client configuration files as viable exploitation vectors.
Until protocol engineers deploy such native safeguards, institutional operators must recognize that validating operations carry distinct execution liabilities. Protecting base deposited collateral is no longer sufficient to guarantee the ongoing flow of returns.
If validation operators fail to implement multi-signature governance over client configuration parameters, repeated fee redirection incidents will force recurring emergency exits, pushing realized annual staking yields below the baseline 2.5% threshold.
This article is for informational purposes only and does not constitute financial advice.