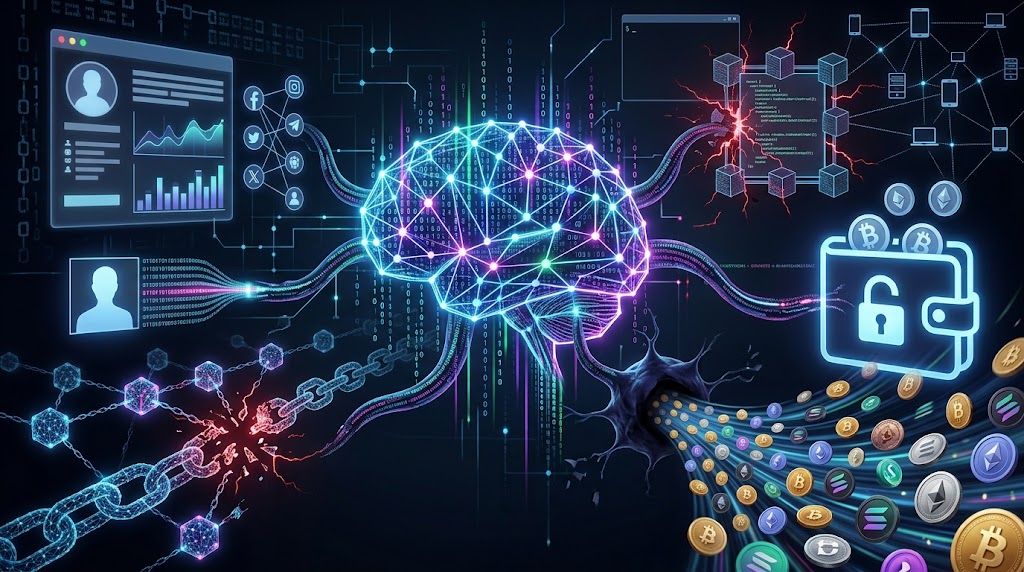
The deployment of advanced generative models establishes an asymmetric advantage for cyber adversaries across decentralized ecosystems. Rather than compromising cryptographic algorithms directly, automated tools accelerate peripheral infiltration against administrative workflows, as evidenced by the official FBI internet crime report.
Widespread industry assumptions maintain that mathematical consensus and on-chain immutability provide adequate protection against financial losses. Yet malicious tools capable of drafting convincing deceptive narratives and inspecting public repositories in seconds disrupt that paradigm, making it imperative to examine how automation alters digital custody risks.
In 2023, the Internet Crime Complaint Center documented $5.6 billion in cryptocurrency-related losses, marking a 45% increase compared to 2022. This upward trajectory underscores a massive automation of financial deception, facilitated by large language models that generate high-volume social engineering schemes targeting retail and institutional participants.
Industrializing Social Engineering and the Human Vector
Modern attack vectors have abandoned crude phishing templates with obvious grammatical flaws. Threat actors now employ autonomous AI agents conducting cyberattacks to scan developer communications, parse software repositories, and synthesize customized interactions designed to infiltrate development teams and decentralized autonomous organization forums.
Human cognitive blind spots represent the primary failure point across distributed systems. The technical threat report published by ENISA indicates that social engineering constitutes approximately 60% of observed intrusion vectors, with generative artificial intelligence significantly optimizing the execution rate of spear-phishing operations targeting decentralized ecosystems.
Generative tools convincingly mimic the tone, jargon, and syntax of project maintainers. This conversational fidelity creates a critical weakness in human interfaces, allowing malicious actors to manipulate community moderators on Discord or Telegram into granting administrative permissions or executing malicious scripts.
Synthetic media further accelerates this threat vector through deepfake audio and video during live identity checks. When coupled with automated wallet drainers, attacks shift from static deceptive links to responsive, conversational fraud that drains digital assets immediately upon user signature.
Furthermore, automated vanity address generation enables high-speed address poisoning attacks. By generating matching prefix and suffix characters of trusted counterparties, automated scripts flood user transaction histories, tricking users into copying compromised recipient addresses during routine transfers.
Operational vulnerabilities become lethal when private credentials leak during social engineering engagements. The devastating StakeDAO deployer key compromise, which resulted in the fraudulent minting of trillions of tokens, demonstrates how human operational breaches completely invalidate on-chain security parameters.
Automated Vulnerability Discovery and the Defensive Asymmetry
Historically, exploiting decentralized finance required extensive manual research. From The DAO hack in 2016 to the multi-million dollar cross-chain bridge exploits of 2022, security analysts and malicious hackers spent weeks manually auditing compiled smart contracts, tracing reentrancy loops and precision flaws.
Automated parsing engines have compressed this audit timeline drastically. Machine models ingest bytecode, examine abstract syntax trees, and detect exposed logic paths, producing an unprecedented velocity in automated exploits where vulnerability identification and weaponization occur nearly simultaneously.
However, general language models exhibit significant precision deficits in code analysis. An academic whitepaper on LLM contract auditing revealed that GPT-4 uncovered 32 of 73 known DeFi vulnerabilities while generating 740 false positives, illustrating a defensive gap in smart contracts that overwhelms human verification teams.
This structural friction creates an asymmetrical dynamic favoring the adversary. A protocol auditor must thoroughly investigate hundreds of erroneous alerts to avoid halting legitimate production updates, whereas an attacker needs only one verified code flaw to drain collateral from a decentralized lending market.
Conversely, cybersecurity researchers assert that automated machine reasoning ultimately strengthens defensive infrastructure. They argue that autonomous mempool sentinels simulate unconfirmed transactions in real time, detecting reentrancy exploits and executing defensive transaction pauses before miners or validators include malicious calls in blocks.
This perspective carries merit because client-side transaction simulation tools identify unauthorized asset transfers before broadcast. By warning users of malicious state alterations during interaction, browser-level filters prevent wallet drainage even when users encounter spoofed application interfaces.
Similarly, ethical bot frameworks leverage frontrunning algorithms to rescue endangered liquidity pools during active breaches. Yet cyber adversaries continuously modify contract call signatures and use private transaction relays to hide exploit transactions from defensive sentinels.
The assertion that artificial intelligence exacerbates systemic vulnerability would be invalidated if automated formal verification tools successfully eliminate logical errors before mainnet deployment, rendering smart contract exploits commercially unviable and eliminating attack surfaces entirely.
Currently, however, the adoption of automated code completion among developers introduces additional supply chain hazards. Novice programmers utilizing unverified model suggestions frequently incorporate deprecated functions and flawed access controls into production repositories, unwittingly expanding the attack surface.
Governance frameworks in decentralized networks face comparable risks from automated proposal drafting. Machine models can craft seemingly constructive governance proposals that conceal malicious parameter adjustments, enabling governance hijacking before community participants adequately parse complex technical documentation.
Consequently, security architecture must shift away from reliance on individual user vigilance. Web3 systems require account abstraction frameworks with programmatic spending limits, establishing a resilience anchored in mathematical verification that renders automated social engineering and deceptive impersonation ineffective.
If empirical data over the next two years demonstrates that capital losses from credential compromise and synthetic social engineering outpace protocol-level consensus vulnerabilities, evidence will confirm that generative systems expanded cyber adversary advantage primarily by weaponizing human operational vulnerabilities.
This article is for informational purposes only and does not constitute financial advice.