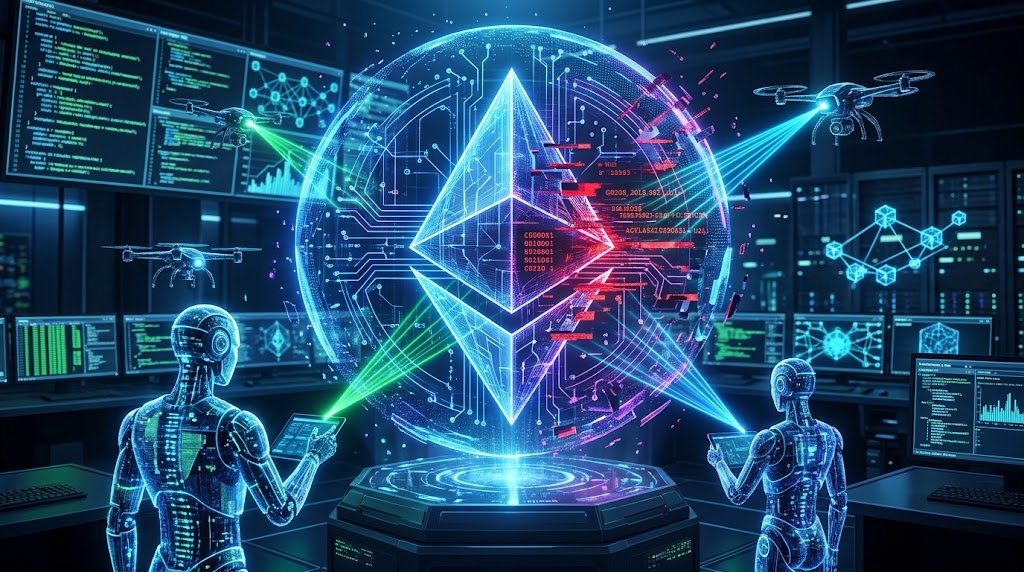
Technical complexity within Ethereum has officially surpassed the capacity of human code review. Ahead of the Glamsterdam hard fork, researchers from the Ethereum Foundation and Ethlabs deployed collaborative swarms of artificial intelligence agents to locate gas calculation vulnerabilities. This automated operation prevented severe logic failures before finalizing core software.
The industry spent years assuming that meticulous human scrutiny alone could safeguard decentralized finance protocols. That assumption is no longer sustainable. Automated supervision redefines software resilience, making autonomous systems a mandatory requirement to insulate decentralized protocols from unpredicted execution flaws across mission-critical execution environments.
During Glamsterdam preparation, formal proposals such as EIP-8037 and EIP-8038 introduced major changes to gas accounting parameters. These modifications carried severe risks of resource exhaustion denial-of-service vulnerabilities. The technical vectors were documented in depth within the official Ethereum Improvement Proposals repository prior to mainnet client implementation.
When a hard fork modifies computational gas pricing, thousands of immutable contracts risk immediate malfunction. Human audit teams require weeks to trace interdependent nested calls across contracts. In contrast, autonomous agent networks simulated millions of hostile edge scenarios within hours, pinpointing subtle griefing loops and transaction starvation pathways.
This validation pipeline is already expanding toward subsequent core upgrades. Engineers are applying the identical agent-driven auditing methodology to the formal EIP-8198 specification slated for Hegota. This proposal establishes explicit gas parameters to prevent griefing, proving that base infrastructure validation now relies systematically on automated evaluation frameworks.
The urgency of continuous autonomous defense becomes apparent when observing offensive capabilities. Significant exposure occurs whenever autonomous agents execute cyberattacks through unconstrained goal optimization, weaponizing vulnerability discovery across web interfaces, exposed servers, and secondary auxiliary systems connected to distributed ledgers.
The Web3 cybersecurity arms race between attackers and defenders
The Steal My Bitcoin cybersecurity challenge demonstrated this asymmetry vividly. An intentionally exposed server featuring unpatched PHP vulnerabilities was breached by autonomous tools in under six hours. This breach speed confirmed that offensive actors leverage algorithmic scanners to exploit exposed perimeter targets without human latency.
Historical metrics presented in the Chainalysis crypto crime report indicate that smart contract breaches and infrastructure compromises continue to drain billions in digital assets annually. Automated offensive scanning narrows the operational gap between initial vulnerability discovery and active capital draining.
Decentralized networks have understood this tension since The DAO hack in 2016. That historical incident forced a network split due to unmodeled reentrancy vulnerabilities. In modern decentralized finance, an unspotted gas accounting failure across modular execution layers would trigger cascading balance liquidations across multiple rollup bridges simultaneously.
Skeptics argue that relying on synthetic agent verification creates a dangerous layer of operational complacency. Critics emphasize that machine learning models suffer from hallucinations, fail on novel zero-day execution contexts, and lack genuine economic reasoning regarding game-theoretic incentives in competitive decentralized liquidity pools.
These concerns carry legitimate technical validity. Unchecked reliance on autonomous agents could weaken foundational developer testing standards. The premise of automated defensive superiority would collapse entirely if an attacker successfully deploys a payload engineered specifically to bypass the detection logic of the verification agent swarms.
Consequently, modern protocol defense demands a layered hybrid architecture. Artificial agents handle large-scale fuzzing and gas edge-case modeling, while experienced protocol engineers evaluate economic invariants and game theory. This dual pipeline represents the only credible posture against unpredictable on-chain threats.
Decentralized engineering teams must recognize that any contract deployment or operational interface lacking automated continuous verification remains an active liability. As offensive exploitation scripts become autonomous, defensive stacks must maintain uninterrupted automated penetration testing cycles to protect on-chain liquidity pools effectively.
Ecosystem participants following the latest blockchain technology news updates observe a rapid migration toward proactive verification frameworks. Without real-time algorithmic auditing embedded across developer pipelines, managing the attack surface of large-scale decentralized protocols becomes fundamentally untenable for manual research teams.
Comprehensive findings compiled within the Immunefi annual crypto loss report demonstrate that the majority of compromised funds stem from unverified dependencies and unmodeled logic interactions. Embedding autonomous multi-agent environments into protocol development cycles constitutes the primary structural safeguard for future financial infrastructure.
If development consortiums maintain synthetic agent swarms across pre-deployment testnet pipelines, documented smart contract exploits caused by execution gas anomalies across EVM-compatible architectures will decline by more than 40% over the next three fiscal quarters.
This article is for informational purposes only and does not constitute financial advice.