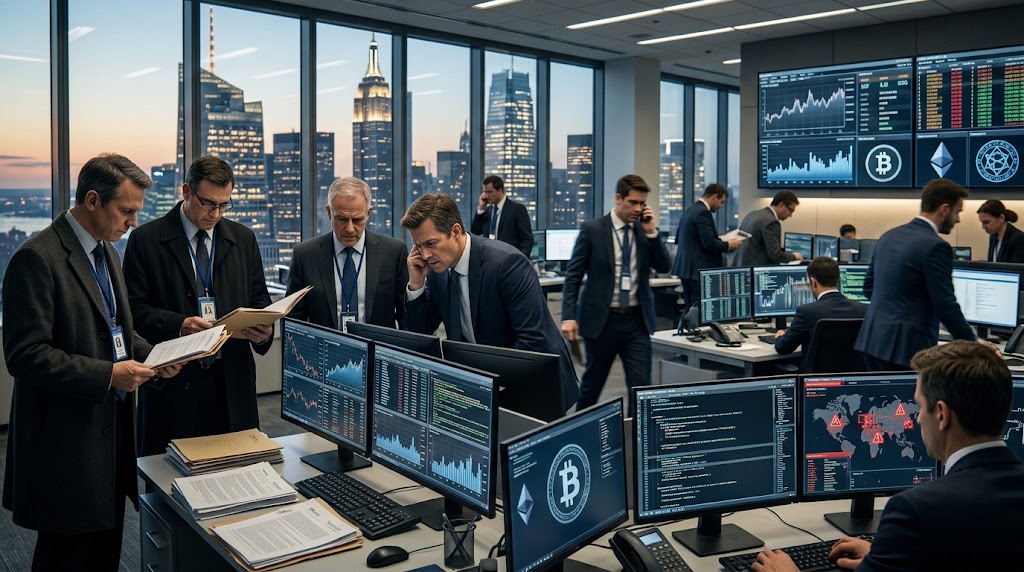
The Federal Reserve and the Office of the Comptroller of the Currency launched reviews across major domestic banking institutions. This supervisory initiative followed the unauthorized extraction of 6.3 billion dollars from Binance, an event that demonstrated structural weaknesses in digital infrastructure security protocols.
Traditional finance previously treated digital asset exposure primarily as a balance sheet counterparty risk. However, the cyber intrusion vectors identified during preliminary investigations reveal that programmatic connectivity between trading desks, liquidity providers, and digital platforms transfers technical vulnerabilities directly into core bank networks.
The primary regulator for national banks detailed expectations regarding external vendor integration within OCC Bulletin 2023-17. This guidance mandates rigorous operational oversight for all shared technological channels interfacing with financial communications and non-bank execution facilities.
Technical forensic logs indicated the attack relied on targeted social engineering, modular malware, and compromised internal artificial intelligence assistance utilities. Information security teams across Wall Street initiated telemetry exchanges to verify whether institutional authentication tokens or API private keys were exposed.
Structural Vulnerabilities and Historical Precedents
Commercial banking previously experienced severe disruptions originating from compromised technical perimeters. In 2016, the cyber robbery targeting the central bank of Bangladesh breached local communications hardware to route fraudulent payment messages totaling 81 million dollars across international messaging rails.
The current incident displays higher velocity due to immediate settlement characteristics in distributed network architectures. Comprehensive infrastructure threat assessments published in the CISA Cybersecurity Advisory highlight how state-sponsored and advanced criminal groups exploit administrative automation tools to bypass standard multi-layered perimeter defenses.
Entities like JPMorgan Chase and Bank of America maintain technical interfaces for settlement flows linked to institutional custodial networks. Regulatory scrutiny now evaluates whether common code libraries or automated software development pipelines allowed remote reconnaissance across segregated institutional banking networks.
Regulators from the Federal Reserve are examining whether employees with access to wholesale payment systems interacted with breached vendor support environments. Traditional banking models treated third-party digital networks as external conduits, ignoring dependencies created by shared cloud services.
Counterpoints and Potential Transmission Scenarios
Banking technology executives maintain that institutional core networks operate under strict zero-trust frameworks isolated from commercial retail architectures. They emphasize that mandatory hardware security modules and multi-signature authorization routines prevent remote execution of unauthenticated commands within internal ledgers.
This defense holds merit when applied strictly to clearing operations on regulated payment rails. The thesis of direct operational contagion would be invalidated if supervisory examinations determine that no shared authentication tokens or administrative conduits were accessed during the intrusion.
Nevertheless, operational threat telemetry documented within the FBI Internet Crime Report demonstrates that sophisticated actors routinely leverage access from adjacent technology partners to navigate enterprise perimeters through synthetic impersonation and hijacked internal workflows.
Institutional resilience standards formulated under the NIST Cybersecurity Framework 2.0 require comprehensive mapping of third-party dependencies across critical systems. Ongoing technical reviews will define whether commercial banks face mandatory restrictions regarding programmatic links with digital asset venues.
If upcoming Federal Reserve compliance audits confirm that shared administrative software or communications pipelines permitted unauthorized access attempts during the last billing cycle, supervisory agencies will mandate structural firewalls limiting direct programmatic connections between regulated clearing banks and offshore digital platforms.
Este artículo tiene fines informativos y no constituye asesoramiento financiero. / This article is for informational purposes only and does not constitute financial advice.