The confirmation of unauthorized hardware implants in devices sold by authorized distributor CryptoBilis triggered cryptocurrency thefts surpassing 86 to 90 million dollars. This breach demonstrates that secure chip architecture provides negligible protection whenever physical supply chain custody fails before delivery.
For more than a decade, the digital asset sector operated under the assumption that network isolation guaranteed security. Intercepting devices within intermediate distribution networks shifts the threat model from malicious software to physical logistics, rendering conventional defenses ineffective against concealed modifications.
Evaluating this vulnerability is critical because thousands of investors acquired these units to exercise absolute financial sovereignty. When hardware arrives pre-modified, private seed generation occurs before an undetected adversary who extracts recovery mnemonics without triggering firmware flags.
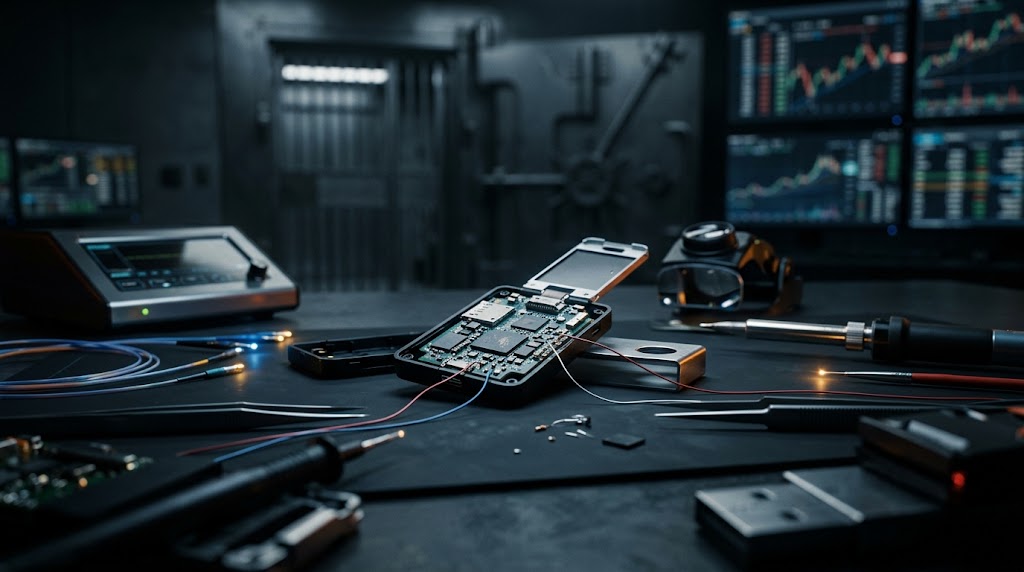
The official investigation documented by SecurityWeek hardware implant coverage reports that attackers manually soldered microcontrollers behind Ledger displays. This module recorded pixel data corresponding to the 24-word recovery phrase during onboarding, exfiltrating credentials over cellular frequencies.
Because the secure element remained uncompromised, the manufacturer’s cryptographic handshake authenticated the hardware as genuine. Consequently, Ledger instructed CryptoBilis to immediately halt all inventory distribution while international investigations proceeded.
For an extensive architectural review of distribution channel vulnerabilities, explore why cold self-custody fails when physical delivery channels suffer unauthorized interception.
Last-mile supply chain vulnerabilities
The technical standard NIST SP 800-161 Revision 1 categorizes risks associated with supply chain tampering across commercial hardware lifecycles. It emphasizes that reliance on external distribution tiers introduces physical interception vectors that software verification cannot remediate.
Historically, physical interdiction was restricted to well-funded state intelligence operations. The CryptoBilis exploit proves that board-level hardware alterations are now deployed by organized cybercrime syndicates targeting retail devices with factory-grade shrink-wrap finishes.
An average consumer cannot disassemble surface-mounted electronics or deploy diagnostic x-ray tools prior to device initialization. Security assurances therefore collapse into blind trust in third-party couriers, customs checkpoints, and local regional distribution facilities.
These structural hazards coincide with institutional expansion into tokenized capital environments. Developments highlighting how tokenized equity asset supply accelerates on public chains illustrate institutional preference for infrastructure governed by enterprise controls rather than individual hardware maintenance.
Opposing perspectives maintain that this incident does not invalidate self-custody principles, categorizing it merely as localized merchant malfeasance. Proponents of this view argue that sourcing hardware directly from European manufacturing facilities eliminates intermediate tampering risks.
However, this counterargument overlooks the fact that CryptoBilis was an officially accredited partner listed on vendor portals. Channel authorization provided zero mechanical defense against deliberate hardware modification throughout the storage lifecycle.
Institutional alternatives and the custodial paradox
The operational fragility of personal cold storage presents a compelling commercial opening for regulated financial structures. Form S-1 filings for the iShares Bitcoin Trust at SEC detail that custody responsibilities are managed by regulated entities like Coinbase Custody Trust Company.
For institutional allocators and high-net-worth participants, regulated depository frameworks backed by commercial insurance remove physical hardware risk. Managing physical cryptographic signers is increasingly viewed as an unnecessary liability compared to regulated vehicle shares.
This dynamic challenges the longstanding foundational ethos that equates direct key control with ultimate safety. Sourcing individual electronic hardware has introduced points of failure resulting in irreversible balance depletion without regulatory protection.
This thesis would be disproven if hardware wallet designers successfully roll out transparent resin enclosures or verifiable open-hardware enclosures that enable visual circuit auditing. Such packaging would eliminate the concealment of daughterboards beside ribbon connectors.
Furthermore, multi-vendor multisignature security models neutralize individual device compromise. Even if an adversary intercepts a single screen ribbon, an isolated implant cannot reconstruct quorum requirements spread across distinct manufacturers.
If cold storage providers fail to enforce cryptographically verifiable transit packaging within the next eighteen months, institutional custodian adoption will absorb over forty percent of long-term retail balances seeking refuge from physical hardware vulnerability.
This article is for informational purposes only and does not constitute financial advice.