Self-custody is widely promoted as the ultimate safeguard for digital assets without financial intermediaries. However, blind trust in physical intermediaries dismantles cryptographic security whenever consumer hardware is intercepted and altered before initial device setup.
🚨 Please get in contact with us ASAP if your funds were drained to these addresses. @SEAL_911 Telegram: [@]seal_911_bot https://t.co/YsJxbFEZt7
— Security Alliance (@_SEAL_Org) October 9, 2026
Recent on-chain drains linked to altered hardware distributed by Southeast Asian reseller CryptoBilis revealed this exposure. Technical assessments verified by the security alliance _SEAL_Org estimate total losses between 72 and more than 86 million dollars across victim addresses.
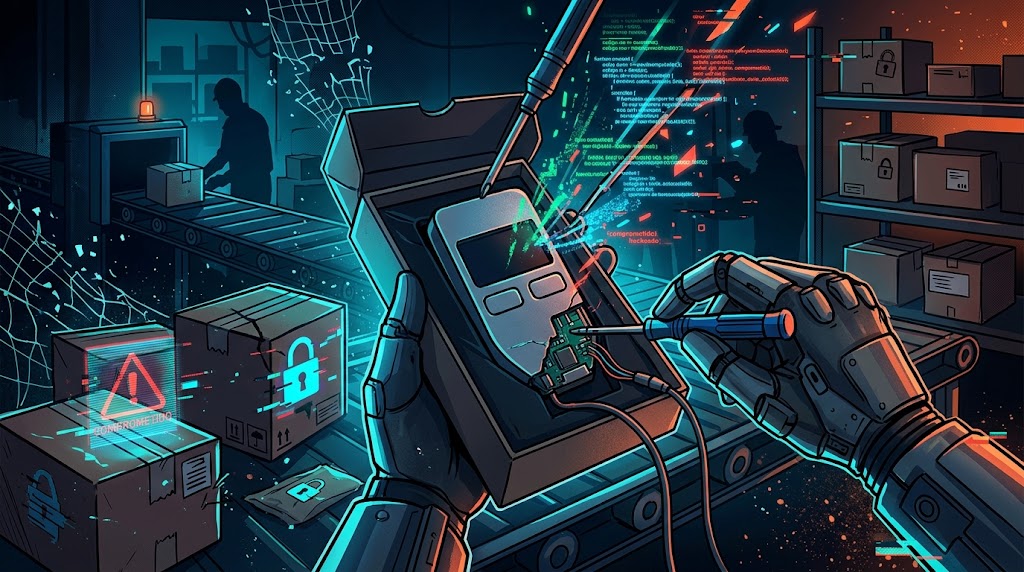
This breach did not stem from cryptographic bugs or protocol flaws inside underlying decentralized networks. Instead, attackers targeted the physical distribution pipeline, swapping internal hardware components or flashing malicious loaders prior to customer delivery.
The principle «not your keys, not your coins» assumes that internal entropy generators operate without external surveillance. When an unauthorized party tampers with a microcontroller, the secure element environment is rendered entirely ineffective before funds are deposited.
This vector exposes an operational paradox across the Blockchain landscape. Investors buy cold hardware to avoid central exchange counterparty exposure, yet inadvertently rely on unverified couriers, warehouse personnel, and regional retail networks.
The breakdown of air-gapped security in global logistics
Hardware manufacturers rely on regional resellers to reduce shipping expenses and bypass import complexities. This distribution strategy fragments operational oversight, creating clear operational opportunities for sophisticated actors to intercept packages and reprogram device logic undetected.
If you were just drained to any of the following addresses, please can you reach out to @SEAL_911 asap. Total loss is >$72M+ and increasing.
TK6DWNpNe1w2iJRNFpU8aHdrPTATxvXT6C
TBkcUMYC7CkTK99tkTnaStQVBastfrs9d9
TCGE3xp6YGRKXxDZiLfysgJW3f22KfMNsW…— tanuki42 (@tanuki42_) October 9, 2026
Independent analysis by security researcher tanuki42_ highlighted that physical inspections fail to detect advanced modifications, catching buyers who purchased items from verified merchant directories. Holographic stickers and shrink-wrap fail as cryptographic verification tools.
Physical supply chain exposures mirror historical data leaks that compromised user privacy. In 2020, compromised e-commerce databases leaked client home addresses, triggering sustained phishing initiatives and physical extortion campaigns across multiple regions.
Vulnerabilities extend beyond capital extraction from smart contracts in Defi. Law enforcement statistics documented by Cointelegraph Magazine revealed over 90 physical attacks targeting cryptocurrency holders over a seven-month span in France alone.
Hardware manufacturers frequently dispute this vulnerability by emphasizing cryptographic device attestation. They maintain that modern secure chips query internal certificates and reject unsigned firmware whenever connected to legitimate management software.
That argument holds against rudimentary tampering attempts and unauthorized firmware flashing. It fails against sophisticated board swaps where peripheral controllers feed falsified handshake responses directly into official desktop interfaces.
Verification burdens and structural distribution reforms
Expecting retail users to inspect microcontrollers under magnification or run bus probes is unrealistic. If authenticating physical security requires laboratory diagnostics, practical self-custody ceases to be viable for everyday market participants.
Hardware wallet builders must reevaluate decentralized distribution strategies to curb retail attack surfaces. Factory-direct delivery mechanisms, tamper-evident silicon packaging, and multi-party computation multisig architectures offer robust alternatives that eliminate single-point physical hardware dependencies.
If hardware wallet providers migrate toward verifiable dual-vendor multi-signature architectures and phase out unmonitored reseller networks by 2027, aggregate supply chain exploits should contract significantly over comparable reporting cycles.
This article is for informational purposes only and does not constitute financial advice.