A clean smart contract audit does not guarantee financial protocol solvency. Traditional code reviews identify software syntax errors and execution bugs, but routinely overlook economic vulnerabilities in smart contracts that emerge when applications interact with external liquidity and volatile market conditions.
The prevailing industry assumption equates bug-free programming logic with total financial resilience. This premise collapses by failing to recognize that misaligned economic incentives allow sophisticated exploiters to siphon vault reserves without violating a single operational line of smart contract code.
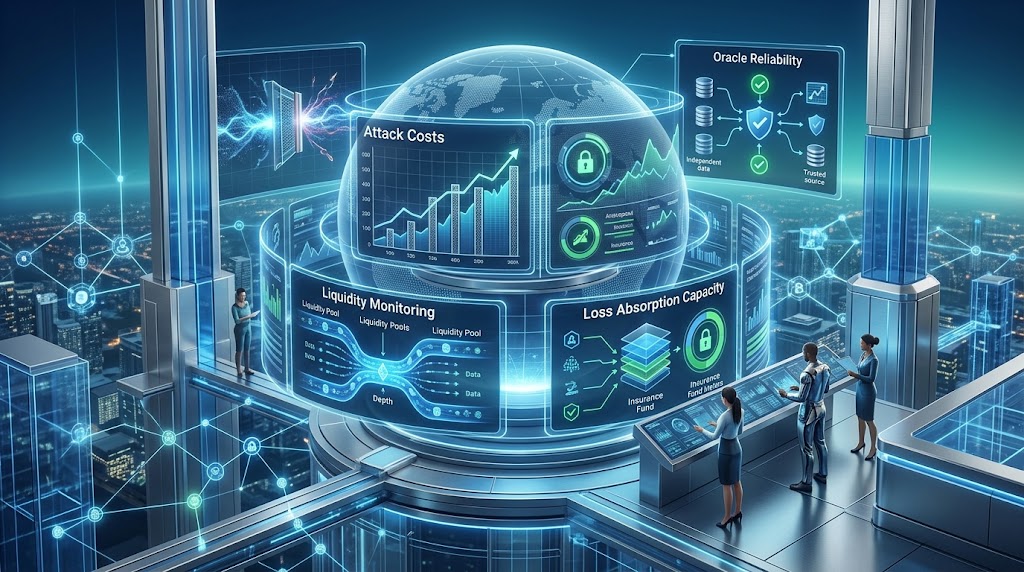
Assessing economic security requires calculating the asymmetric ratio between attack cost and extractable capital. If manipulating price mechanisms to extract protocol assets costs less than the harvested collateral value, an economic exploit will occur regardless of how many security firms approved the contracts.
Nominal total value locked frequently presents an illusion of real protocol solvency. Much of that reported volume originates from recursive leverage across decentralized finance, where identical collateral deposits are re-hypothecated across multiple lending markets without proportional underlying balance sheet backing.
True available liquidity must instead be calculated using price slippage tolerance under severe distress. A liquidity pool holding one hundred million dollars nominally may fail to absorb a five million liquidation without causing massive price depreciation across associated collateral markets.
Automated market maker depth dictates resistance against deliberate spot manipulation attacks. As shown by documented concentrated liquidity market mechanisms, compressing capital into narrow trading bands can enable abrupt pricing imbalances whenever large institutional trades rapidly drain thin out-of-range order books.
Capital concentration introduces another critical point of failure that analysts often ignore. When three wallets command over forty percent of active protocol deposits, sudden liquidity withdrawals break baseline collateral ratios, triggering uncontrollable cascading liquidations across connected lending venues.
Decentralized governance systems introduce direct capital vulnerabilities as well. If an attacker borrows significant voting tokens via uncollateralized flash loans to alter risk configurations, treasury reserves can be drained through operations that formally obey all protocol governance rules.
Quantifying Core Economic Security Parameters
Oracle architecture represents the most frequent exploit vector for induced balance sheet insolvency. When lending protocols rely on illiquid spot prices or local decentralized exchanges, market manipulators can artificially pump collateral values within a single atomic transaction block.
Mitigating this structural vulnerability requires independent decentralized oracle feed networks that aggregate price data across deep off-chain and on-chain liquidity venues. Update latency and deviation thresholds dictate whether automated liquidators can execute underwater collateral before bad debt accumulates.
Composability creates compounding counterparty exposures across synthetic derivatives and tokenized debt. These vulnerabilities accelerate alongside the threats of institutional asset tokenization, where legal redemption delays and illiquid real-world assets freeze secondary lending collateral during severe market contractions.
Historical precedent substantiates this fundamental divergence between software integrity and economic solvency. In October 2022, Mango Markets lost 114 million dollars when a trader inflated MNGO token spot prices using under ten million dollars, executing an attack that perfectly obeyed protocol code.
During the March 2020 Black Thursday crash, severe Ethereum network congestion enabled liquidators to seize 8.3 million dollars in MakerDAO collateral for zero DAI. The underlying software executed without technical bugs, but sudden operational liquidity evaporation created systemic insolvency.
Capital loss absorption frameworks distinguish resilient architectures from inherently fragile platforms. Dedicated safety modules, backstop insurance treasuries, and automated protocol deficits absorb bad debt write-offs before retail depositors suffer forced haircut deductions on their deployed capital.
Analytical Boundaries and Counter-Perspectives
A prominent technical counterargument insists on the supremacy of formal code verification. Proponents assert that mathematically proven invariant assertions and exhaustive constraint modeling can restrict protocol execution states, ensuring that anomalous state transitions remain mathematically impossible.
This opposing perspective holds validity within isolated, fully deterministic software environments. If a decentralized application avoids external oracle feeds, maintains no secondary market interactions, and prevents third-party composability, formal verification successfully guarantees that deposited funds remain secure from mathematical exploitation.
However, modern decentralized finance relies upon open, non-stationary market dynamics. As emphasized by fundamental oracle architectural design constraints, external market data lacks absolute on-chain finality, introducing unavoidable discrepancies between reported reference prices and executable secondary liquidation values.
Our thesis would be invalidated if decentralized applications abandoned external composability entirely while establishing closed deterministic exchange ratios. Under that hypothetical architecture, economic security would cease to be a dynamic financial issue and become solely a static software verification problem.
A comprehensive protocol evaluation requires moving past blind reliance on static smart contract certificates. Due diligence must rigorously audit economic parameters: liquidation slippage depth, dynamic reserve requirements, cross-collateral contagion risks, and stochastic stress simulations under sudden market crashes.
If lending protocols holding over one hundred million dollars fail to enforce stress tests modeling thirty percent liquidity drops across secondary markets, bad debt accumulation will exceed forty percent of their operational treasuries during the next severe market drawdown.
This article is for informational purposes and does not constitute financial advice.